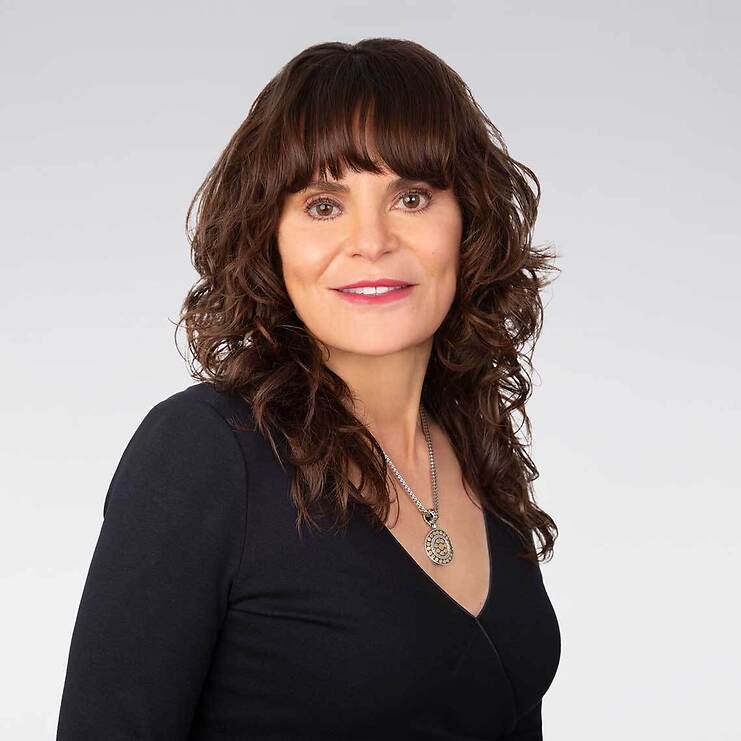
Profile
Sydney counsels clients on cybersecurity and artificial intelligence (AI) public policy, legislation, and regulation, with over 20 years of experience practicing law in these areas. Sydney collaborates with government affairs, legal, cybersecurity, engineering, and technology teams to inform company specific, sectoral, and broader industry advocacy on cybersecurity. She advises clients on designing and implementing compliance plans with new and existing regulatory frameworks.
Experience
Representative Matters
- Advised clients on how to prepare for new cyber incident reporting requirements under the Cyber Incident Reporting for Critical Infrastructure Act (CIRCIA) final rule.
- Collaborated across industry sectors to develop an amendment to the proposed CIRCIA rule definition of a significant cyber incident in collaboration with the U.S. Chamber of Commerce.
- Counseled client on a successful strategy to change the direction of a federal agency project on 5G privacy and security and tailor the scoping of reports to reflect existing industry workstreams.
- Advised client on and drafted industry recommendations for telecommunications carrier use of AI.
- Helped clients navigate AI-driven vulnerability sharing and applicability and renewal of the Cybersecurity Information Sharing Act of 2015.
- Developed a comprehensive overview of and recommendations on legal and regulatory risks of delayed migration to post-quantum cryptography.
- Collaborated with client cybersecurity and legislative teams and industry associations, to deliver prevailing, clearly articulated and technically precise advocacy on cybersecurity best practices, critical infrastructure regulation, and supply chain amendments to the National Defense Authorization Act (NDAA) in multiple years.
- Collaborated with client cybersecurity and legislative teams to develop a successful alternative to an NDAA amendment dictating the use of specific wireless technologies and security measures in the provision of service by contractors overseas.
- Advised client on the protection of critical infrastructure information (PCII) and limitations on scoping during planning and execution of a tabletop exercise with the Cybersecurity Infrastructure and Security Agency, and recommendations involving GPS jamming, network timing, and UAS.
- Advised client on compliance strategy for FCC national security regulations and decisions regarding the Secure Equipment Act Covered List and supply chain limitations applicable to government contractors.
- Successfully guided Internet coalition’s policy priorities during in-person negotiations and built consensus among companies, industry groups, privacy and civil society groups, and academics on the NTIA Multistakeholder Mobile App Transparency Code of Conduct.
- Managed and negotiated eight cybersecurity bills enacted into law as House Homeland Security Cybersecurity Subcommittee counsel.
Professional Experience
- Principal Analyst, T-Mobile (2022-2023)
- Vice President, Public Policy & Government Relations, Internet Security Alliance (2021)
- Counsel, House Committee on Homeland Security (2020-2021)
- Private law practice (2001-2018)
- Pro Bono Counsel, U.S. Army and U.S. M.C. Veterans (2010-2017)
- General Counsel, Taste of the South (2006-2010)
- Legislative Assistant, U.S. Representative Ed Whitfield (2000-2001)
- Law Clerk, U.S. Senator Sam Brownback (1998-2000)
- Summer Associate and Law Clerk, Private law practice (1997-1998)
- Legislative Assistant, Private law practice (1993-1996)
Affiliations
- Federal Communications Bar Association (FCBA)
Practice Areas
Credentials
Education
J.D., Columbus School of Law, The Catholic University of America
B.A., Emory University
Bar and Court Memberships
- District of Columbia Bar
Related News & Insights
- AlertCold Storage, Hot Targets: Hackers Hit French Fridges and Dutch DeliveriesJacqueline F. "Lyn" Brown, Mary Beth Schultz, Erin M. Joe, Sydney M. WhiteOctober 23, 2026
- AlertExecutive Order Rebrands AI as “Super Intelligence” and Signals Potential Federal Legislative ChangesJacqueline F. "Lyn" Brown, Sydney M. White, Teresita R. Kummer, Alissa Lynwood, Ania Trichet, Kevin T. NguyenOctober 2, 2026
- Blog PostLooming Incident Reporting Mandates: Who Needs to CareWiley ConnectMegan L. Brown, Jacqueline F. "Lyn" Brown, Sydney M. White, Joshua K. WaldmanSeptember 14, 2026
- AlertAI-Driven Vulnerability Sharing: Four Takeaways on “Gold Eagle” and Other New InitiativesDuane C. Pozza, Kathleen E. Scott, Sydney M. White, Alissa LynwoodSeptember 3, 2026
 Cookie Preference Center
Your Privacy
When you visit our website, we use cookies on your browser to collect information. The information collected might relate to you, your preferences, or your device, and is mostly used to make the site work as you expect it to and to provide a more personalized web experience. For more information about how we use Cookies, please see our Privacy Policy.
